Understand the risk.
Improve the controls.

Authorized assessments with evidence, remediation, retesting and clear testing limits.

Back to the homepage

Security needs evidence.
Not promises.

Web engineering informed by hands-on security research. We trace relevant controls, document evidence and explain what remains outside the review.

Define a security review
  1. 01

    Scope & authorization

    Agree assets, test identities, demonstration data, traffic limits and written authorization before testing.

  2. 02

    Review & assessment

    Review authentication, access control, input handling and configuration using OWASP categories relevant to the scoped features.

  3. 03

    Remediation & retest

    Findings describe root cause, evidence, impact and recommended fixes. Retesting checks the same controls after remediation.

  4. 04

    Technical handover

    Reports distinguish validated findings, hypotheses, testing limits and residual risk. No website is claimed to be 100% secure.

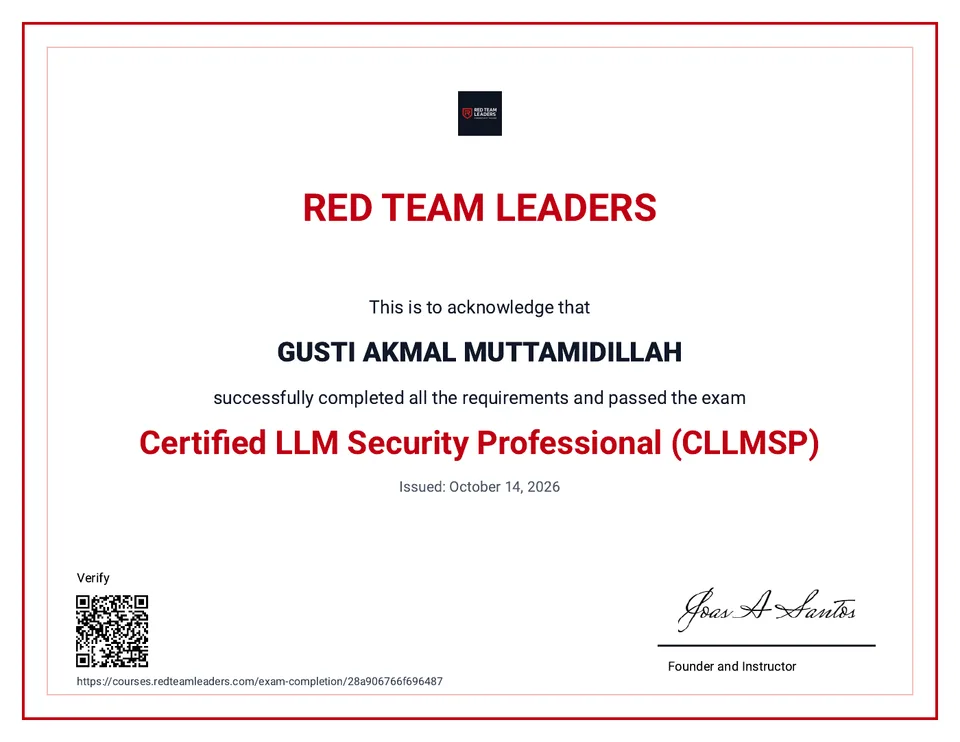
Certified LLM Security Professional (CLLMSP)

Awarded to Gusti Akmal Muttamidillah on 14 October 2026. This is the developer's credential, issued after passing the Red Team Leaders exam.

Verify with issuer ↗ View certificate (PDF) ↗
CLLMSP certificate for Gusti Akmal Muttamidillah, Red Team Leaders, 2026

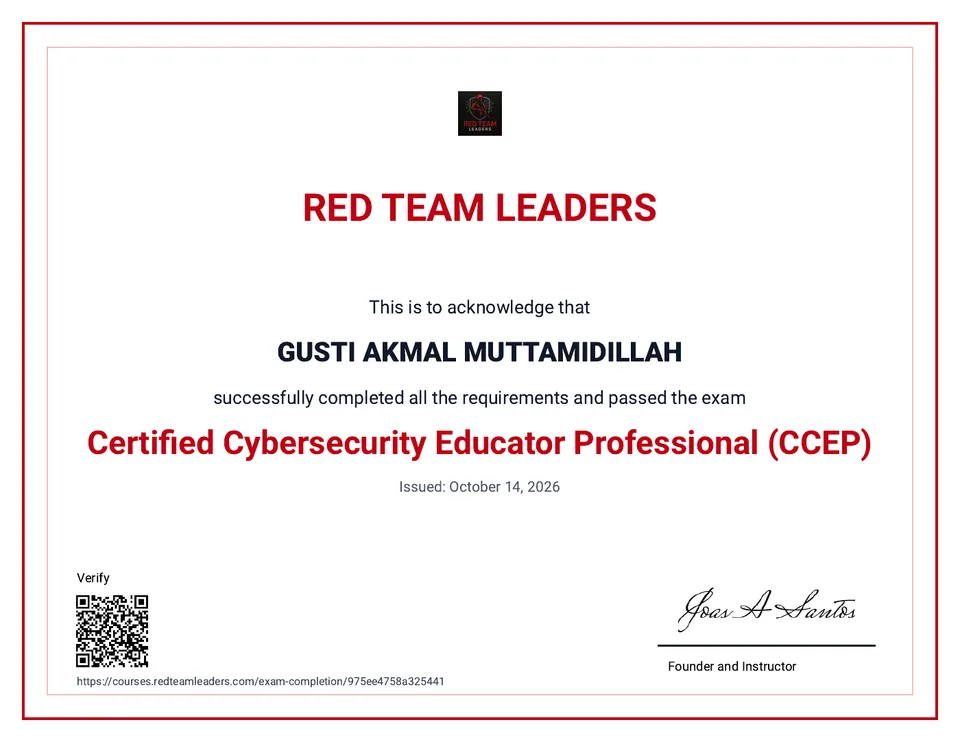
Certified Cybersecurity Educator Professional (CCEP)

Awarded to Gusti Akmal Muttamidillah on 14 October 2026 after passing the Red Team Leaders exam. This is the developer's credential.

Verify with issuer ↗ View certificate (PDF) ↗
CCEP certificate for Gusti Akmal Muttamidillah, Red Team Leaders, 2026

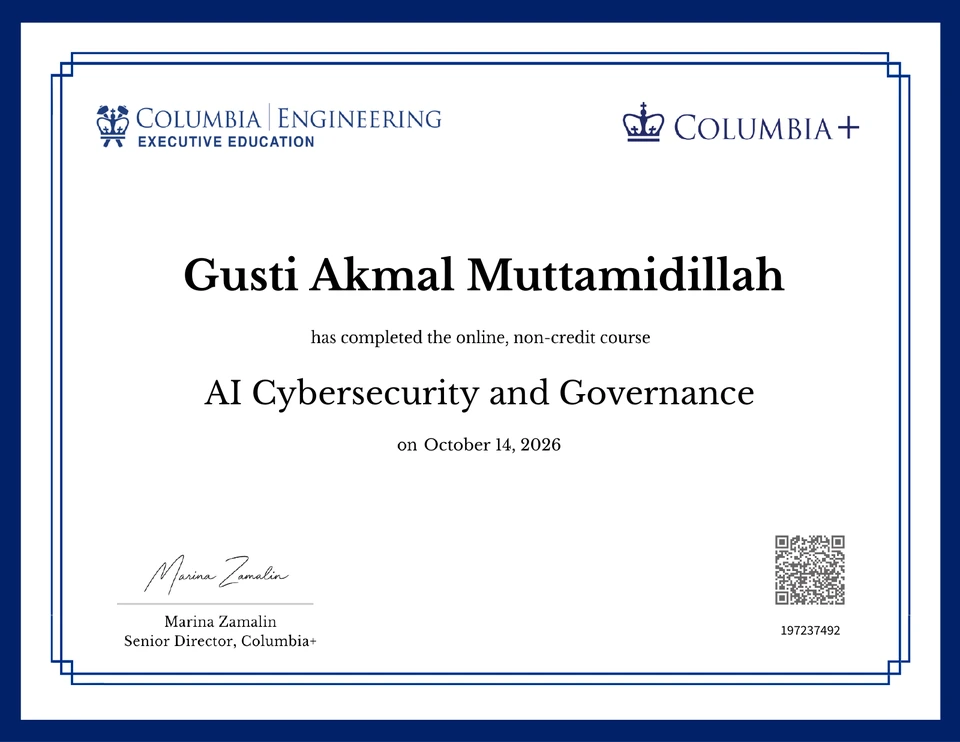
AI Cybersecurity and Governance

Online, non-credit course completed by Gusti Akmal Muttamidillah on 14 October 2026. Issued by Columbia Engineering Executive Education / Columbia+. Certificate ID: 197237492.

View course certificate (PDF) ↗
Columbia+ AI Cybersecurity and Governance course certificate for Gusti Akmal Muttamidillah, 14 October 2026

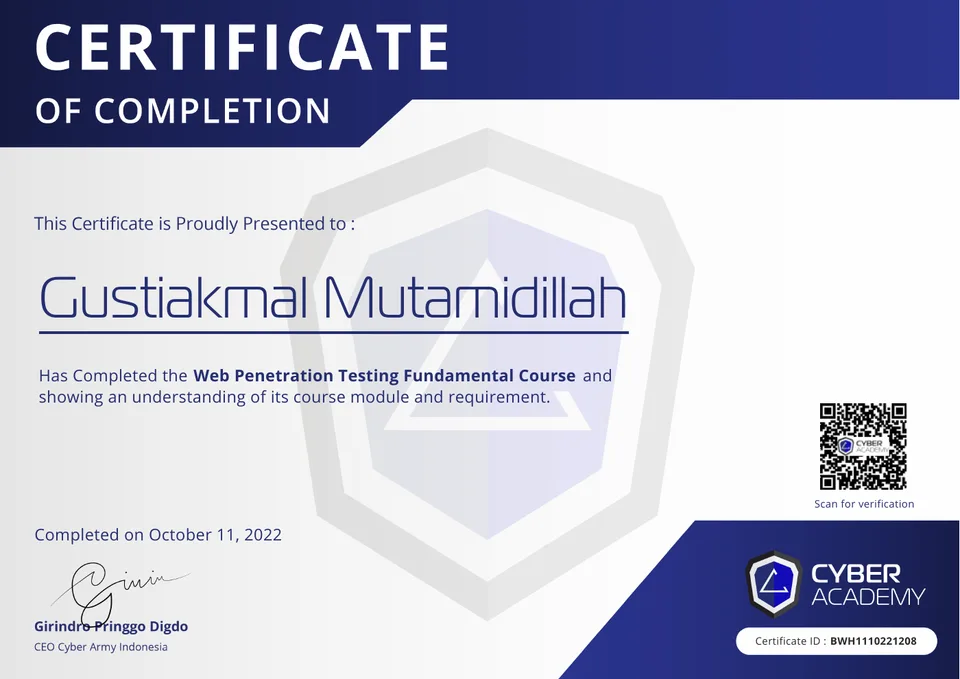
Web Penetration Testing Fundamental Course

Completed by Gustiakmal Mutamidillah on 11 October 2022. Certificate ID: BWH1110221208.

View course certificate (PDF) ↗
Cyber Academy Web Penetration Testing Fundamental course certificate for Gustiakmal Mutamidillah, 2022

techindo.com

Authorized, time-bounded external assessment of the exact origin. The archive contains 78 first-party HTTP requests and independently reviewed evidence.

Read the full audit report (PDF) ↗

The sample validated no impactful security finding or exploit chain. A search input formed a new HTML attribute, but the offline browser check did not execute the sentinel. Anonymous API requests were rejected, tested logins did not create an admin session, and search comparisons did not demonstrate SQL injection.

Backend source, comparative test accounts, and owner-side database, queue, and mail observations were unavailable. The result applies to the tested sample, not the whole site.

Security research case study

The redacted version of the complete technical case study covers three historical candidates, evidence limits, and source appendices. Target, provider, account, and credential values appear as ***.

Read the evidence and limits ↗
Download full redacted case study (PDF) ↗

The archive directly shows a client-side configuration with a public anonymous role. Audit notes describe sensitive API reads, but raw admin and data API responses are absent. Access-control impact and present-day exposure cannot be independently confirmed from this folder alone.
Full case study and evidence status

Directly inspectable

An archived client bundle contains a public anonymous-role configuration. A separate probe note records sign-up and authentication error messages. Neither item proves unauthorized access to private data; public anonymous keys are expected in this architecture.

The audit notes list 492 API keys and 604 user profiles in admin results, plus 604 profiles, 11 payments, 528 messages, and 1,251 credit transactions in anonymous-role results. Individual keys, identities, and record values are shown as *** in the PDF. These numbers are from the notes, not independently verified raw responses.

The audit notes report unauthenticated admin reads and anonymous data reads. The folder does not retain the corresponding raw HTTP exchanges, role controls, or a later retest. No write or account takeover impact is claimed: the recorded write probes used nonexistent IDs and changed no rows.

Independent security reviews

01QUICK CHECKIdentify public configuration issues before deciding what to fix.From$149/ assessment

Included scope

  • One website/domain; non-intrusive public configuration review
  • HTTPS/TLS, security headers and relevant exposure
  • Findings summary and recommendations
Discuss QUICK CHECK ↗

Boundaries

Not a full pentest. Excludes login testing, exploitation and security certification.

02STANDARD REVIEWReview login, user access and input handling within an agreed application scope.From$499/ assessment

Included scope

  • One application with agreed endpoint and role limits
  • Authentication, sessions and access control where available
  • Input handling and important configuration checks
  • Report with severity and recommendations
Discuss STANDARD REVIEW ↗

Boundaries

Written authorization is required. Assets, roles, endpoints and testing window are agreed before assessment; retesting is separate unless included.

03ADVANCED REVIEWReview web/API workflows with technical evidence and agreed retesting.From$999/ assessment

Included scope

  • Authorized web/API review
  • Authorization, business logic and multi-role testing as scoped
  • Technical report, findings evidence and remediation guidance
  • Limited retesting when included in the proposal
Discuss ADVANCED REVIEW ↗

Boundaries

Asset count, roles, testing time and deliverables are defined in the proposal. No guaranteed findings, certification or vulnerability-free claim.

04CUSTOMRequest Custom Quote

Included scope

    Discuss CUSTOM ↗

    Boundaries

    Scope is agreed in the proposal.

    From a conversation
    to a working website.

    1. 01

      Understand the business

      Discuss website goals, audience, content and operational constraints before selecting features.

    2. 02

      Agree the scope

      Record deliverables, fees, timeline, revisions, hosting and testing limits in a proposal.

    3. 03

      Design & develop

      Review the visual direction, then implement it in a preview you can use.

    4. 04

      Check & refine

      Review user journeys, mobile behavior, performance and agreed security controls. Address issues before handover.

    5. 05

      Launch & hand over

      Release after approval. Transfer source code, documentation and agreed access.

    Website
    questions answered.

    Read the website planning and cost guide
    Are hosting and domains included?

    Yes. Website packages include hosting and one .com domain for the first year. Renewals after the first year are charged separately.

    What do I need to provide?

    Prepare your business name, a short description of your services or products, your logo if available, photos, and contact details. We help arrange the content.

    How long will it take, and how many revisions are included?

    Business Website takes about 1–3 weeks and Growth Website about 2–5 weeks once content is ready. Custom application timing and your revision allowance are listed in the quote before you order.

    Can I manage the website myself?

    Yes, if you choose a package with an admin area. We provide guidance for the included updates, such as products, services, or photos.

    How is maintenance different from a security review?

    Basic covers only basic monitoring, SSL/domain checks and monthly reports; it excludes managed backups, technical updates and incident handling. Business adds scheduled backups and controlled updates as agreed. Secure Care adds basic security checks and priority communication during service hours, excluding full pentesting and unlimited incident response. Security Review is a separate assessment with an agreed scope and written authorization.

    What do I receive from a security review?

    A report of the checks performed, evidence for verified findings, and recommended fixes.

    Can you work on an existing website?

    Yes. Send us your website address. We review it, then explain the recommended changes and their cost.

    Need a website
    for your business?

    Business Website starts at $750, including hosting and one .com domain for the first year. Tell us about your business and target launch date. We will help you choose a package.

    Include +country code for international numbers.

    After a successful submission, your requirements are saved and you can continue the conversation on WhatsApp.